Video Gratis Demo Ethical Hacking & Cyber Security dengan Informasi CVE Terbaru, Terpopuler dan Terlengkap di Dunia yang merupakan produk dari X-code (PT. Teknologi Server Indonesia)
Highlights CVE Terbaru (2026):
Eksploitasi Nginx (CVE-2026-42945) – Reverse Shell pada web server populer.
Heap Buffer Overflow di MariaDB (CVE-2026-32710) – Dampaknya hingga Persistent Privilege Escalation (UDF RCE).
Privilege Escalation Ubuntu (CVE-2026-31431 & Dirty Frag CVE-2026-43284/CVE-2026-43500) – Celah pada kernel Linux yang membahayakan banyak sekali server di tahun2 026.
Eksploitasi Telnet (CVE-2026-24061) – Celah pada protokol klasik yang masih sering ditemukan.
Reworking Exploit Kernel FreeBSD (CVE-2026-7270)
🔥 Topik Populer & Menarik Lainnya:
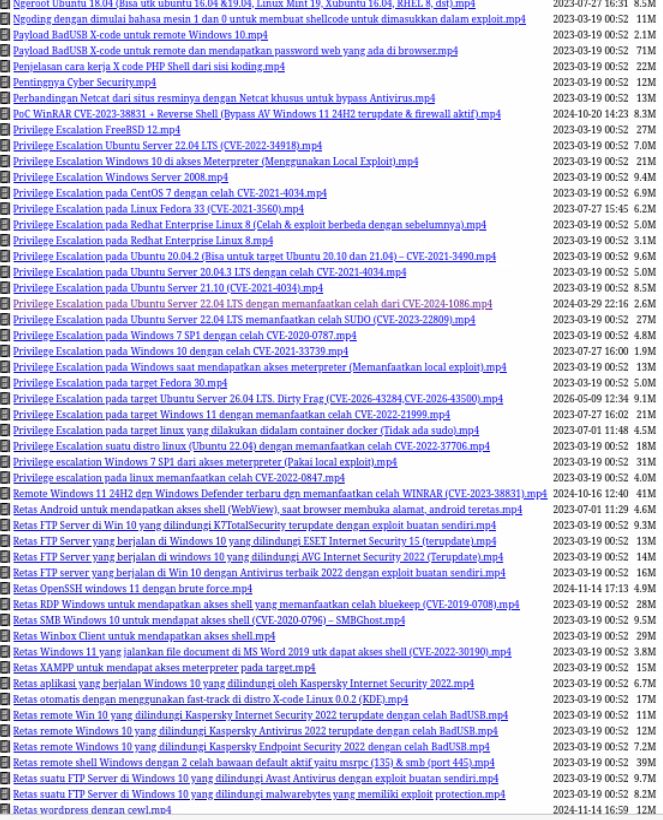
Privilege Escalation (Rooting) – Multi Platform: Beragam demo untuk Linux (CVE-2021-4034, CVE-2022-34918, CVE-2024-1086), Windows (CVE-2020-0787, CVE-2021-33739, CVE-2022-21999), FreeBSD, OpenBSD 6.6 (yang terkenal super aman), hingga metode di dalam container Docker.
Bypass Antivirus: Menunjukkan bagaimana teknik mutakhir dapat melewati berbagai antivirus ternama seperti Kaspersky, Windows Defender, Panda, ESET, Malwarebytes, AVG, Avast, dan K7TotalSecurity.
Web Application Security: SQL Injection (manual & POST method), XSS (Persistent & DOM-Based), RFI, SSRF, XXE, CSS Injection, serta eksploitasi pada CMS populer seperti WordPress, Joomla, Laravel, Apache Tomcat, & Webmin.
Mobile & IoT: Demo cara mendapatkan akses shell di Android (WebView) dan eksploitasi pada router MikroTik (Winbox & backup config cracking).
Network Security: Demonstrasi serangan man-in-the-middle seperti ARP Spoofing, SSL Stripping, dan sniffing hash Samba.
💻 Fokus: Teknik Mendapatkan Remote Shell
Reverse Shell Windows 11 24H2 Terbaru – Firewall aktif, Windows Defender update terbaru, semua proteksi hidup.
Remote Shell via MS Word (CVE-2022-30190) – Eksploitasi Follina, cukup buka dokumen Word, shell langsung dapat.
Remote Shell via WinRAR (CVE-2023-38831) – Bypass AV Windows 11 24H2 & firewall aktif.
Remote Shell via Notepad++ (CVE-2025-49144) – Eksploitasi aplikasi editor populer di Windows 11.
Remote Shell via Log4Shell – Eksploitasi celah Log4j pada web server.
Remote Shell via Apache 2.4.49 (CVE-2021-41773) – Path traversal yang berujung RCE.
Remote Shell via PHP Disable Function Bypass – Bypass restriksi PHP 7 & 8 untuk mendapatkan reverse shell.
Remote Shell via XAMPP – Mendapatkan meterpreter pada target yang menjalankan XAMPP.
Remote Shell via Webmin (CVE-2022-36446) – Eksploitasi pada panel admin populer.
Remote Shell via SMB (SMBGhost CVE-2020-0796) – Eksploitasi protokol SMB Windows 10.
Remote Shell via RDP (BlueKeep CVE-2019-0708) – Celah klasik pada Remote Desktop Protocol.
Remote Shell via React2shell (RCE) – Dari pengenalan, scanning bug, hingga eksploitasi.
Shell via Winbox MikroTik – Eksploitasi pada router MikroTik.
Dan masih banyak lagi, ratusan video.
Akses Gratis: https://video.xcode.co.id